Investigating Conduct Incidents: From Report to Resolution
Learn how SMEs can investigate conduct incidents: log reports, triage risks, identify root causes and document corrective action through to resolution.
A Corethix guide for growing businesses
Conduct incident investigation is the structured process of logging, triaging, investigating and closing reports of staff misconduct or control failures. It establishes what happened, why it happened, what corrective action is needed and whether that action was completed. For SMEs, an unresolved or undocumented incident can create regulatory, employment and reputational exposure.
Many smaller businesses handle conduct issues informally: a quiet word, an email thread, a decision nobody wrote down. That approach might feel efficient, but it leaves no trail to show what happened, why, or what was done about it. A clear investigation record helps a business explain its response to regulators, insurers and employment tribunals.
In this article
- Why incident investigation is a conduct risk control
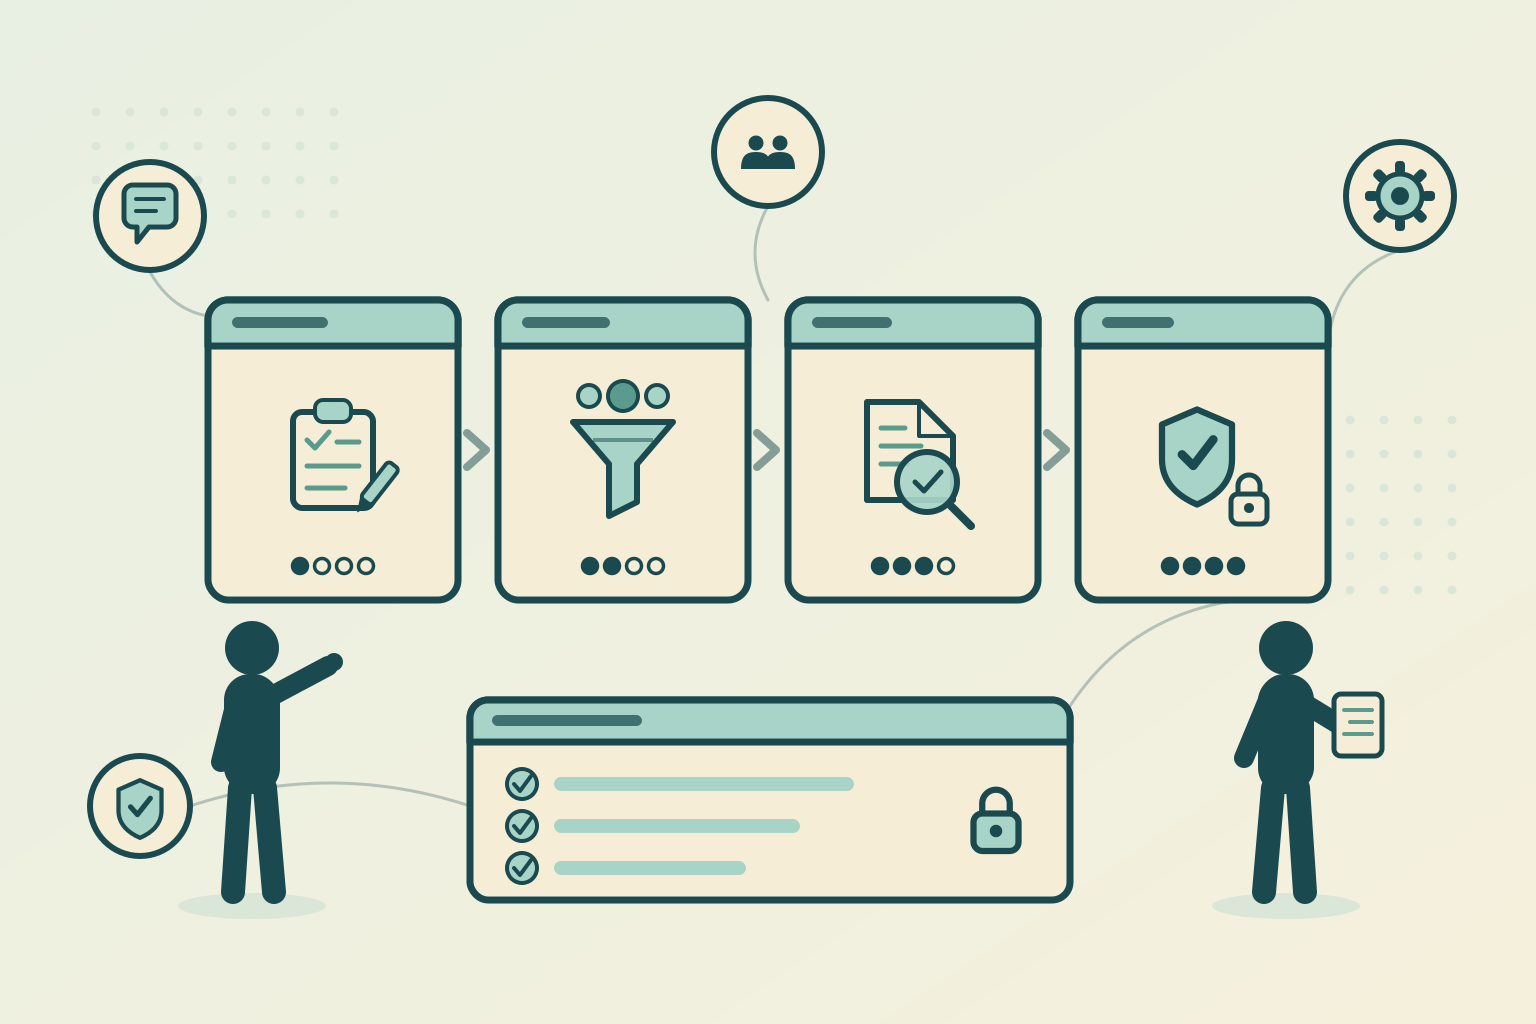
- The four-stage process: log, triage, investigate, close
- Non-financial misconduct under the FCA's COCON 1.1.7FR
- Building a process that fits a small team
- Frequently asked questions
Why incident investigation is a conduct risk control, not an HR afterthought
It is tempting to treat a conduct incident—a mis-sold product, a data slip or a complaint about a colleague's behaviour—as a one-off people problem to be handled quietly and moved past. But every incident is also a data point about whether your controls are working.
A single missed know-your-customer (KYC) check might be an isolated error. Three missed checks by the same team in two months may indicate a control failure. You only spot the pattern if every incident is logged consistently in one place rather than resolved individually and forgotten.
Investigation discipline also protects the business when things go wrong later. If a former employee raises a tribunal claim, or a regulator asks how a complaint was handled, the question is rarely just “what happened”—it is “what did you do about it, and can you show your working?” A business that can produce a dated log, a triage decision, an investigation note and a closure record is in a fundamentally different position to one that can only offer a manager's recollection.
If your business does not yet have a defined process, Corethix incident management software can support a lightweight approach your managers will actually use. For the wider context, read our guide to conduct risk management for SMEs.
The four-stage conduct incident investigation process
A workable incident process has four stages. The size of your business changes how much time each takes, not whether it happens.
1. Log the incident
Every conduct-relevant incident—a complaint, a near-miss, a reported behaviour issue or a control breach—goes into one central log as soon as it is known, not after it has been informally resolved. Capture the date, source, a short description, who is handling it and its current status.
2. Triage the report
Not every incident needs a full investigation, but every incident needs a triage decision, made quickly and recorded. Triage asks: how serious is this, who needs to know, and what response does it warrant?
A minor process slip might need a quick corrective conversation. A pattern of complaints, a potential regulatory breach or an allegation involving a senior person needs a more formal response, likely with someone independent of the area involved.
3. Investigate the facts and root cause
A proper investigation establishes the facts, identifies the immediate cause and—critically—asks what allowed it to happen. An investigation that stops at “the adviser made an error” misses the underlying gap: was training inadequate, was the process unclear, was workload too high, or was there no second-check control?
Key takeaway: A conduct incident that is logged but never triaged, root-caused or closed out is not a resolved risk. Recording an incident is only the beginning of managing it.
4. Close the incident with evidence
Closure means recording the outcome, the corrective action taken and who approved it, and confirming the action was actually completed—not just agreed. An incident marked “closed—action agreed” with no follow-up remains an unresolved risk.
The new pressure point: non-financial misconduct under COCON 1.1.7FR
This section concerns relevant UK FCA-regulated financial-services firms, not every SME or jurisdiction. From 1 September 2026, the FCA's new rule at COCON 1.1.7FR extends the scope of the conduct rules in non-banking firms to cover serious bullying, harassment or violence against colleagues where there is a sufficient work-related link.
The rule does not have retrospective effect. Firms should assess earlier conduct under the Handbook provisions that applied at the time. The practical lesson is to record and assess reports consistently, establish the relevant facts and seek appropriate compliance or legal advice about the applicable rules.
Read the official FCA guidance on non-financial misconduct and Policy Statement PS25/23 for scope, implementation and detailed guidance.
Building an investigation process that fits a small team
You do not necessarily need a dedicated case-management system to start. A simple tracker or access-controlled spreadsheet can provide a foundation, provided someone owns it and it is reviewed on a fixed schedule—not only when something goes wrong. Sensitive allegations and personal information should only be accessible to people who need them.
A practical incident log should include:
- Date reported and source of the report
- Short description of the incident
- Triage decision, priority and escalation requirements
- Investigator or responsible owner
- Findings and supporting evidence
- Root cause and any control gaps
- Corrective action, action owner and due date
- Evidence of completion, approval and closure date
Give one senior person clear ownership of the log itself, separate from whoever investigates an individual incident, so nothing quietly falls off the list. Review open items monthly, or sooner where the urgency warrants it, and bring a short summary of incident volumes and themes to leadership at least quarterly.
A two-line “what we saw and what we did about it” can be more useful than a lengthy narrative. Feed recurring themes back into your risk register and update relevant policies and procedures.
Frequently asked questions
Does every complaint need a full investigation?
No. Every conduct-relevant incident needs a recorded triage decision, but the depth of investigation should be proportionate to its seriousness, potential harm and any recurring pattern, rather than applied uniformly to everything logged.
Who should investigate a conduct incident?
Someone with suitable competence, sufficient authority and, ideally, independence from the area or individual involved. For very small firms, this may mean a director or an external adviser handling allegations involving senior staff.
What counts as serious non-financial misconduct under the FCA rule?
The FCA rule covers serious misconduct with a sufficient work-related link within its defined scope. Seriousness must be assessed in context using the FCA's guidance, rather than assuming that every workplace disagreement is a conduct-rule breach or that a formal complaint is always necessary. Relevant firms should consult the current Handbook and obtain advice where needed.
How long should we keep conduct incident records?
Set a documented retention period based on the applicable regulatory requirements, employment claim time limits and privacy obligations in your jurisdiction and sector. There is no single retention period suitable for every SME. Keep records securely and obtain advice before deciding when to delete them.
What is the biggest mistake SMEs make with incident handling?
Resolving the immediate issue informally and never logging it. This leaves no reliable record of the response and makes it harder to spot when the same root cause resurfaces.
The bottom line
An incident that is handled well but never logged may leave a later reviewer unable to distinguish it from an incident that was not handled at all. The fix is not more process for its own sake: it is a consistently used log, a clear triage step, root-cause investigation where needed and a closure record proving the action actually happened.
Get those four habits right and you have both a better-run business and a defensible record of your response. If you would like help setting up an incident investigation process that is proportionate to your size and easy for managers to follow, contact Corethix.
This article provides general information, not legal advice. Regulatory and employment obligations depend on your jurisdiction and sector.